Authorized network administration
How to use Nmap to find open ports
Nmap is a network discovery and port-scanning tool. Install it from the official Nmap project or a trusted operating-system package source and verify the package. The original guide used the Windows Zenmap interface; the examples below retain its useful command-line concepts.
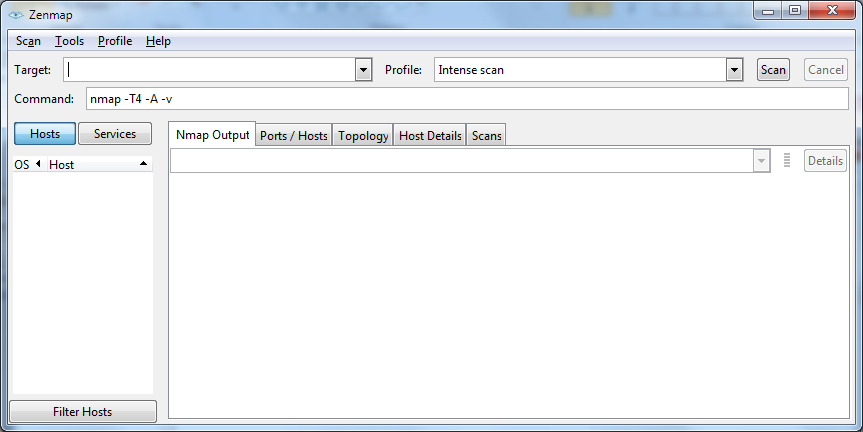
Options used in the original guide
| Option | Meaning |
|---|---|
-T0 through -T5 | Timing templates from very slow to very aggressive. Do not assume -T4 is safe; choose a rate appropriate to the approved environment. |
-sS | TCP SYN scan. It commonly needs elevated privileges and remains detectable. |
-sU | UDP scan, which can be slow and may produce ambiguous open/filtered results. |
-sS -sU | Requests both TCP SYN and UDP scanning. Modern Nmap documents these as separate options rather than the old guide's combined spelling. |
-p T:161,U:161 | Selects protocol-specific ports. |
-iL targets.txt | Reads targets from an operator-reviewed file. |
-oN report.txt | Writes normal human-readable output. |
-oX report.xml | Writes XML output. |
-oA report | Writes normal, XML and grepable output using one basename. |
--append-output | Appends rather than overwrites supported output files. |
--open | Shows hosts that have an open, open/filtered or unfiltered port. |
-n | Disables reverse DNS resolution. |
Prepare a reviewed target file
Nmap target files may contain one authorized target expression per line: an IPv4 address, hostname, CIDR network, IPv6 address or supported octet range. Keep this file under access control and confirm that every entry is in scope before execution.
Examples from the original walkthrough
These examples are templates. Replace the paths and target file only after scope review. Start conservatively; the original -T4 timing has been changed to -T3.
Check TCP port 161
nmap -T3 -sS -p T:161 -iL C:\input.txt -oN C:\output.txt --append-output --openCheck UDP port 161
nmap -T3 -sU -p U:161 -iL C:\input.txt -oN C:\output.txt --append-output --openCheck TCP and UDP port 161
nmap -T3 -sS -sU -p T:161,U:161 -iL C:\input.txt -oN C:\output.txt --append-output --openCheck an approved TCP port list
nmap -T3 -sS -p T:21-25,80,139,161 -iL C:\src_netlist.txt -oN C:\ports_out.txt --append-output --openCheck TCP ports plus UDP 161
nmap -T3 -sS -sU -p T:21-25,80,139,161,U:161 -iL C:\src_netlist.txt -oN C:\ports_out.txt --append-output --openSave XML or all output formats
nmap -T3 -sU -p U:161 -iL C:\input.txt -oX C:\output.xml --open
nmap -T3 -sU -p U:161 -iL C:\input.txt -oA C:\output --open
Write scan files outside public webroots. Hostnames, banners and script output may be attacker-controlled, so treat every exported report as untrusted input.
Open Nmap XML in Excel
Older Excel versions may ask whether to apply the stylesheet referenced by the XML.
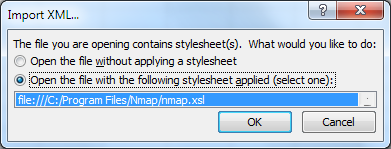
A local stylesheet reference may fail when Nmap is installed at a different path.
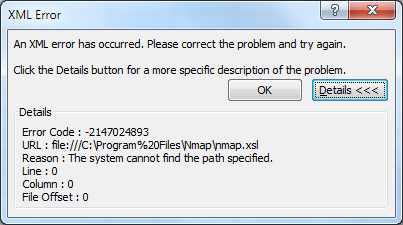
An external document-type declaration may also be blocked by modern XML security controls.
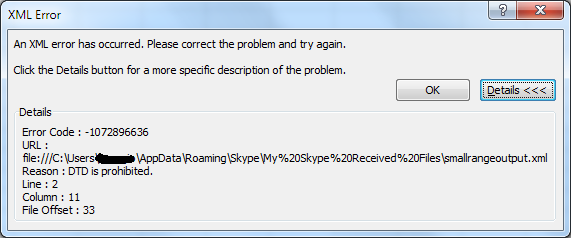
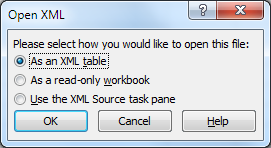
When available, opening without a stylesheet and choosing an XML table gives a basic tabular view.
Opening normal text output in a spreadsheet
The original guide described replacing line endings and labels in a text editor before import. That is fragile because Nmap records can span varying numbers of lines. Prefer XML and a bounded parser designed for Nmap output. If text must be imported, work on a copy and verify host and port record counts afterward.